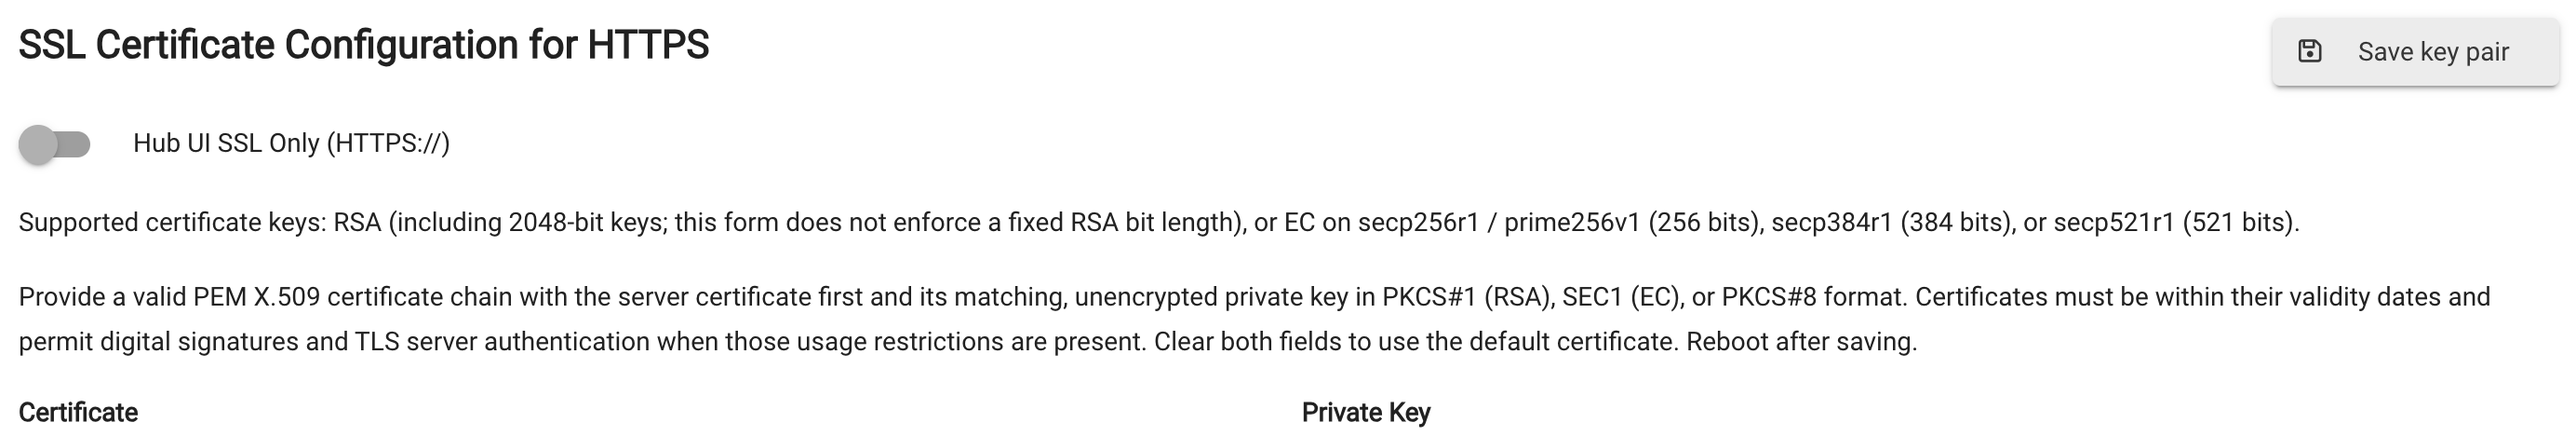
I've updated my SSL cert on the Hubitat via /hub/advanced/certificate and saved the key pair successfully.
After the reboot, I cannot reach my Hubitat via https anymore. So, I read the documentation and I couldn't find any restrictions, but it seems that a secp256k1/prime256v1 cert is not supported.
3 things:
Are only RSA certs supported?
If so, why isn't it documented?
Why was the key-pair saved successfully, if it isn't supported? (It shouldn't accept an unsupported cert. If I had SSL-only enabled, this would have bricked my device.)
Thanks for the reply. Luckily I didn't activate the SSL-only flag, thus I was able to connect to it without SSL and install a new RSA cert (EC certs obviously don't work).
But if I had that flag set, it would have locked me out. No idea how you would remotely change something on my device (especially if I can't even login). If you can actually do that we have to have another discussion....
Yes, I would think so too. Successfully saving a cert that is not supported that will then render SSL connections dead is a bug in my book.
It should also be mentioned in the documentation that EC certs are not supported and that only RSA certs with a bit length of X are supported.
It's a flag in the hub's database, and you're not the first person who ran into a "locked out" scenario, so it's a special support case, with a special tool to deal with it. As long as the hub is connected to the cloud (which can be disabled in Settings), we can help turn the flag off. You should also be able to disable it locally by running the /hub/advanced/disablessl endpoint.
The fix got a proper error message, but I'll add the "which certificates are supported" tidbit to the screen, too.
Now I am very confused. This message states that EC keys are supported. Why did it kill my SSL then when I uploaded a prime256v1 key? Then the bug was not accepting an unsupported key, but killing SSL with a non-RSA one.